Search, import and export
Finding things and moving data in/out. Availability: both editions.
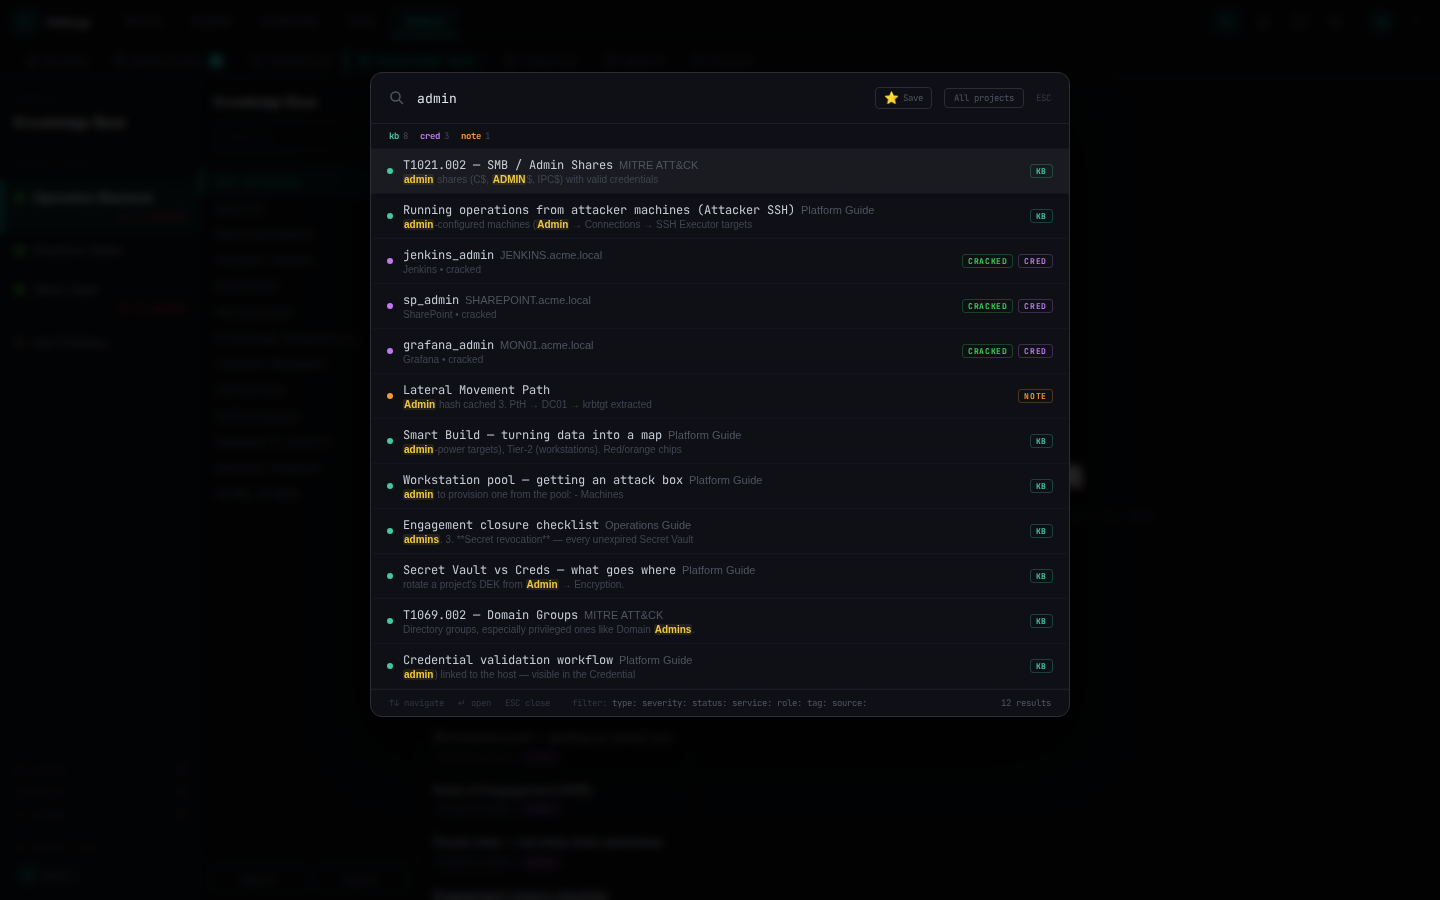
Search (Ctrl+K)
One endpoint searches across hosts, creds, notes, findings, loot, jobs, KB articles and command snippets, scoped to the current project or all projects (toggle).
- Filter syntax:
type:,severity:,status:,service:,role:,source:,connector:,tag:— e.g.type:finding severity:critical,type:cred service:smb,tag:DC - Server-side highlighting; loot titles are blurred in results
- Related objects nested under each row; keyboard navigation opens the target view with the entity focused
- Saved searches — name and re-run queries
Import
| Source | Lands as |
|---|---|
| Project ZIP | full project restore (password when encrypted) |
Nessus .nessus |
hosts, findings |
| Burp XML | findings, hosts |
| BloodHound ZIP | hosts, creds, access edges |
| nmap XML / NetExec text / Advanced Port Scanner | hosts, ports (client-side parsing) |
| Firewall/router configs (Cisco ASA/IOS, Palo Alto, Fortinet, MikroTik, pfSense, Huawei, UniFi) | parsed preview → project enrichment |
| IP/CIDR lists | bulk host import |
See Firewall config export for the vendor matrix and diffing.
Export
| What | Where | Notes |
|---|---|---|
| Full project | Projects → Export ZIP | AES-encrypted when secrets included; one-time password |
| Hosts / creds / findings | CSV per entity | secrets excluded |
| Report | PDF / HTML / MD | Reporting |
| Playbooks (+ packs) | JSON / bundle ZIP | per project |
| KB, snippets, finding templates | JSON | |
| Cred matrix | view in UI | no plaintext export |
Expected behavior
- Imports upsert by natural keys (IP, username+service) — safe to re-run
- Encrypted project exports refuse to include secrets unless the
server has
pyzipper(then they abort loudly, never silently plaintext)