Findings, notes, loot and knowledge
The Output-side evidence store. Availability: both editions.
Findings
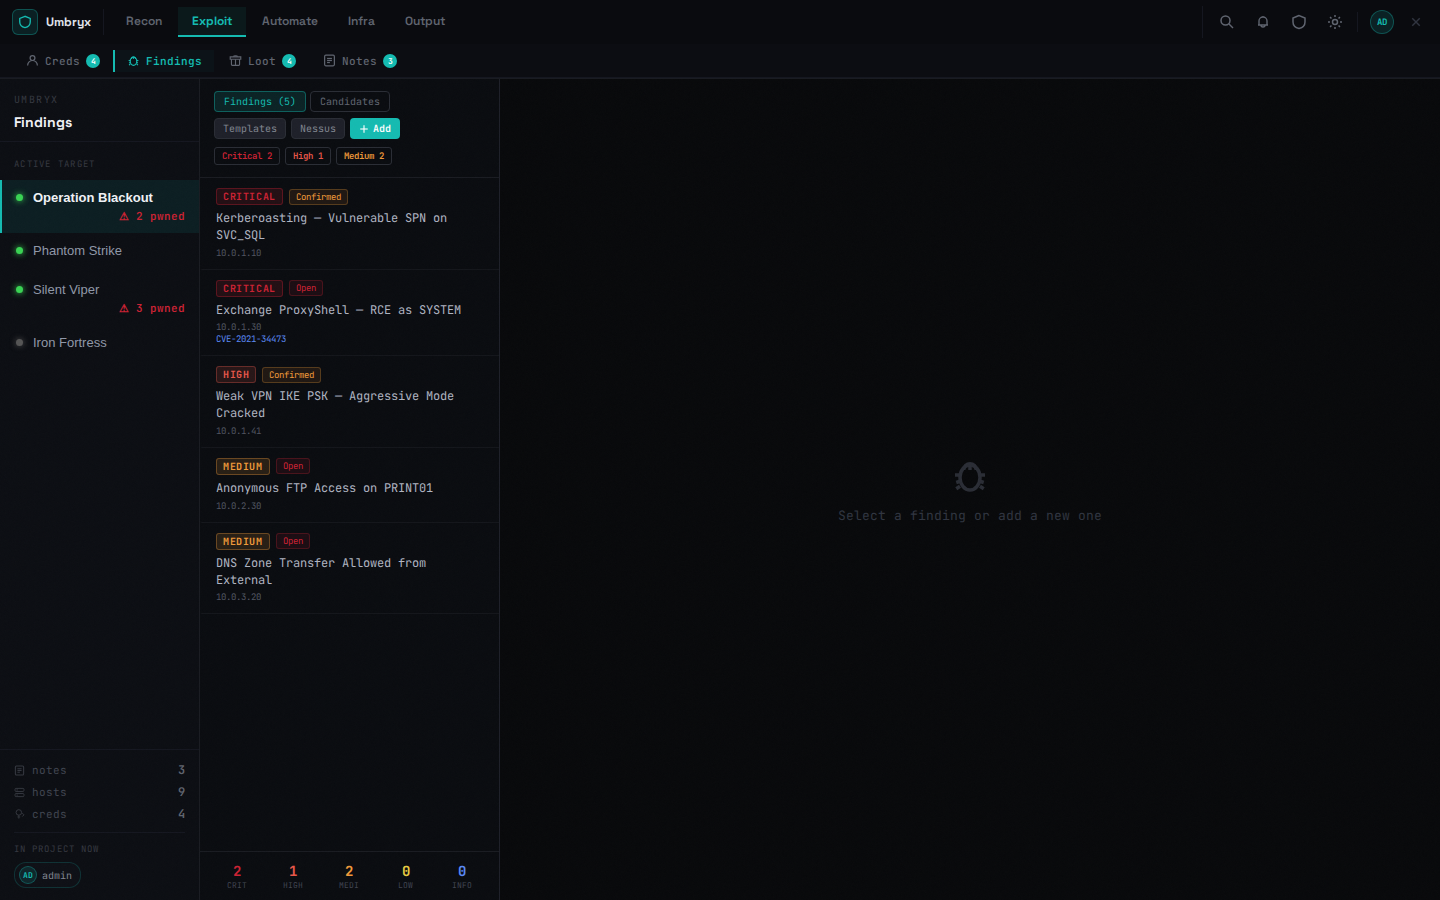
List with severity badges, statuses (open / triaged / confirmed / false_positive / resolved / closed), filters by severity/status/host.
- Form: title, severity, CVSS, CVE, description, proof, recommendation, host link
- Templates library: built-in + custom (JSON import/export)
- Candidates — potential findings extracted from scanner output; convert to findings in one click
- Imports: Nessus and Burp land here (require
findings.create) - Approval: the
reviewerrole ownsfindings.approve
Notes
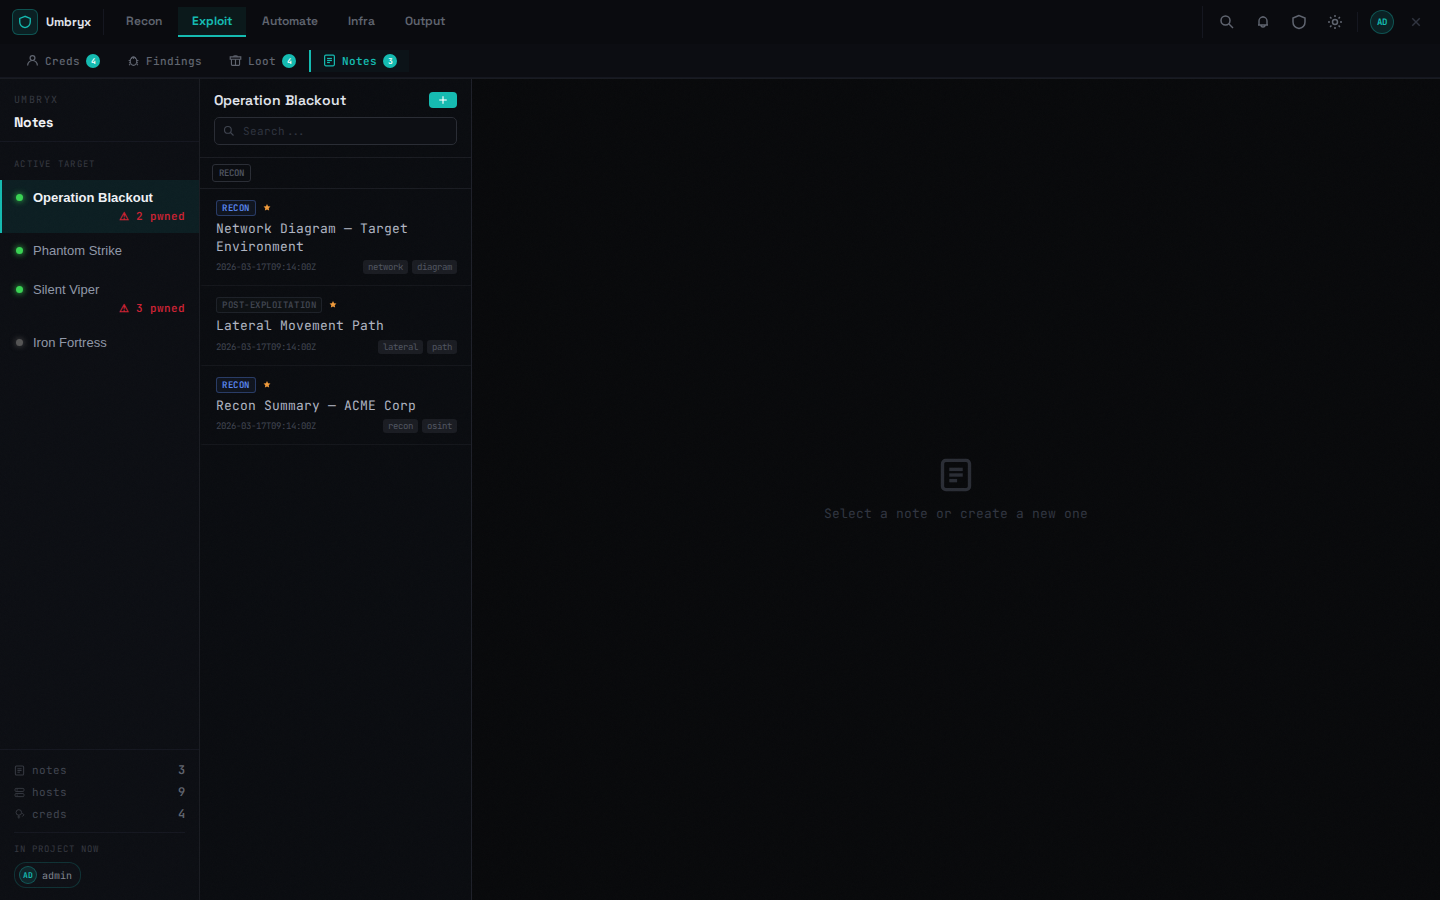
Markdown notes organized by phase (recon → report), tags, stars,
host links, file attachments. Confidential tags (confidential,
secret, sensitive, opsec, restricted) encrypt the content at
rest. Live collaboration: presence avatars and focus events over
WebSocket.
Loot
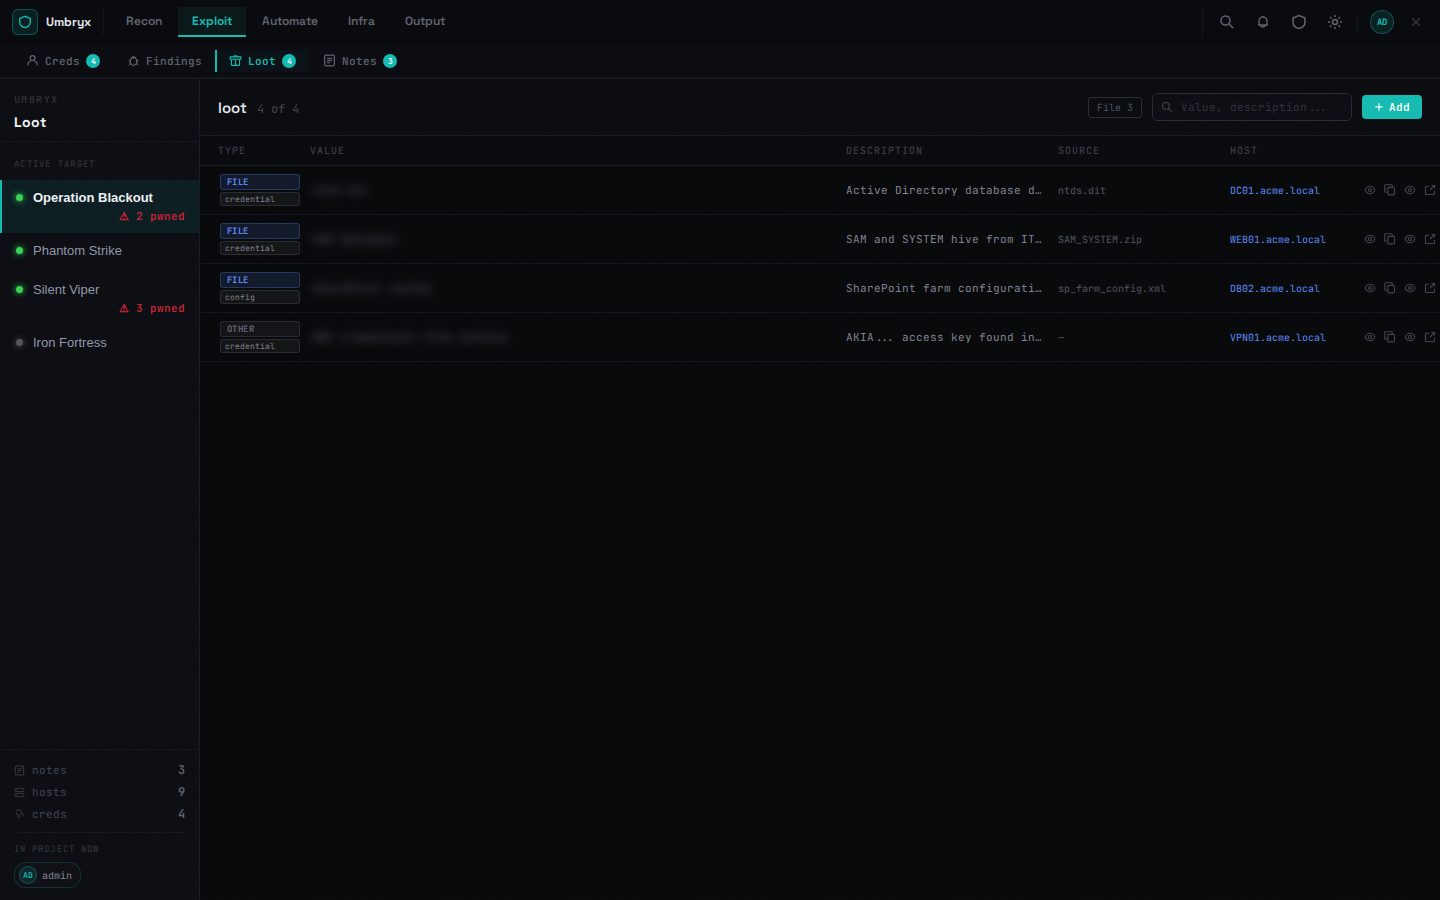
Artifacts with type (file/secret/text/…), filters, and preview (image, PDF, text, sheets, docx; office/database formats are download-only). File loot is encrypted on disk and served decrypted through the authenticated download endpoint. Hashes and secrets found in job output are extracted here automatically. Every loot carries the SHA-256 of its file.
Knowledge base
Markdown articles, project or global scope, categories and tags, search. The MITRE panel surfaces technique articles (used for attack-path autocomplete). JSON import/export for the whole KB.
Checklist and objectives
- Checklist — per-phase task lists with progress; load defaults (LinPEAS, Kerberoasting, testssl.sh, …) or build your own
- Objectives — flags (
flag{…}), BAS and objectives with points, statuses and submission capture confirmation
Expected behavior
- Scanner candidates appear without manual parsing
- Deleting soft-deletes; restore is available and the timeline keeps the audit trail