Credentials, secrets and the Access tab
Availability: both editions. Access: listing creds needs
credentials.read; revealing secrets needs credentials.read_secret
(every reveal is audit-logged).
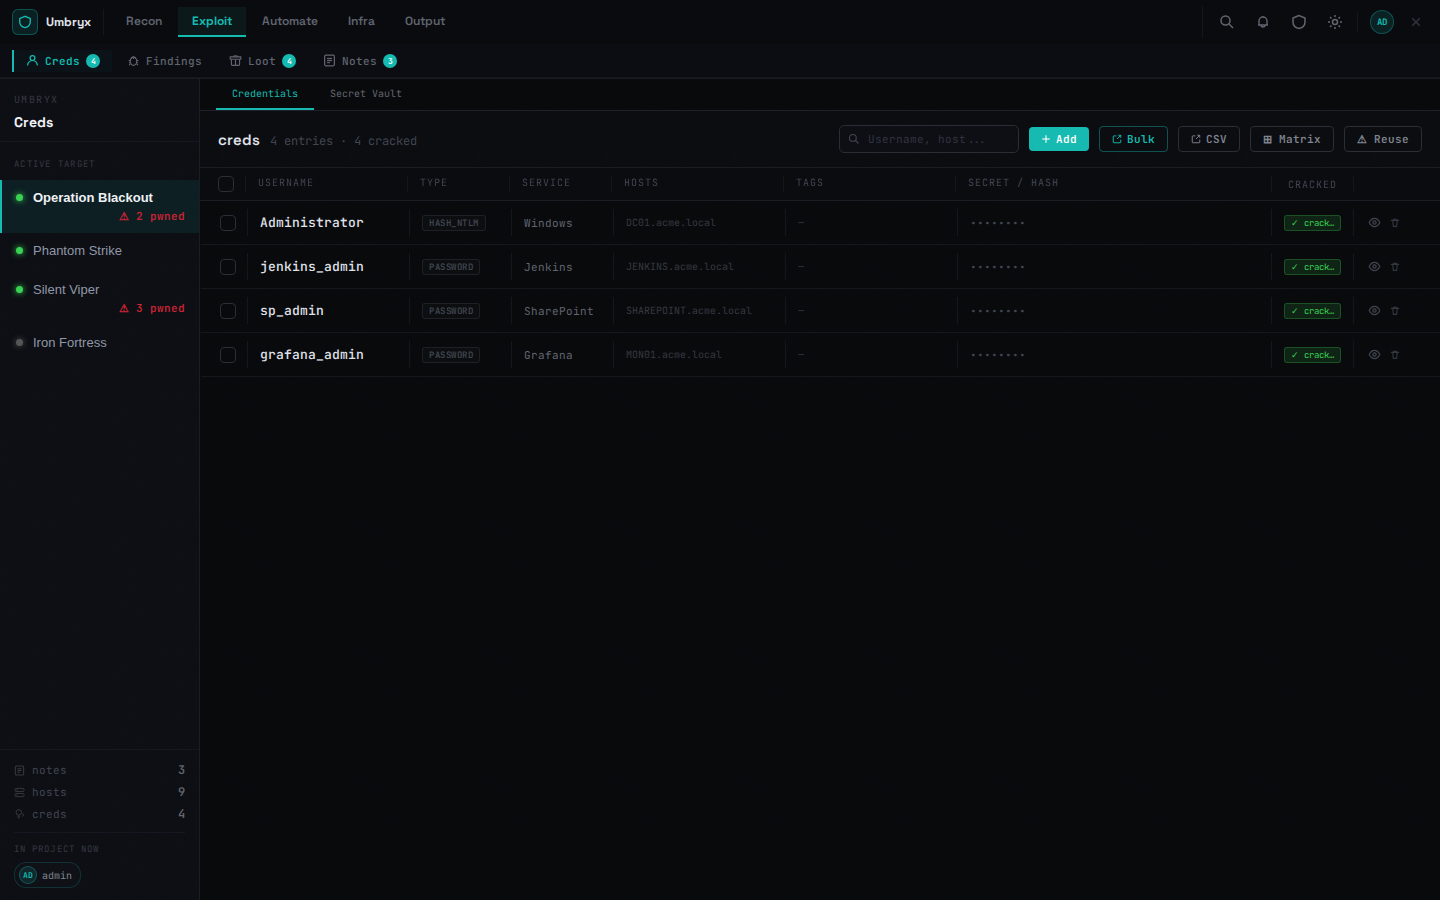
Credentials
Two sub-tabs: credentials and vault.
- Add single or bulk-paste (
username secret type service host
  cracked notes tags
lines) - Views: list (filters by type/domain/tags, search), matrix (creds × hosts), reuse analysis
- Reveal fetches the decrypted secret (
GET /creds/{cid}/secret, rate-limited); copy and hide controls - Domain creds apply to all matching Windows hosts
- Validate runs the cred against selected hosts (SMB/WinRM/SSH/ LDAP/MSSQL/RDP); successes create access edges and finding candidates
crackedtoggle, bulk edit, Export CSV (secrets excluded)
Secrets are stored encrypted with a per-project DEK; roles without
read_secret see metadata only, everywhere (REST, WS, exports).
Vault (project secrets)
Named secrets with lifecycle: create, revoke (marked, audit event), delete, download, and SSH key-pair generation.
Access tab
One screen with everything needed to connect to the project's
infrastructure: C2 connection lines (URL, login, password/token —
decrypted for roles with secret rights), infrastructure service
credentials with stack status, dropped payload links (public pwndrop
URLs + SHA-256), and pool workstations with ready-to-use ssh
commands and "your key is installed" state.
Sources: registered C2 integrations, EE stacks, droppers, pool machines.
Expected behavior
- Every reveal/decrypt is audit-logged (
secret_revealed,read_credential_secrets) - CSV exports never include secret values
- Exporting the project with secrets yields an encrypted ZIP
Limitations
- Reveal is rate-limited (30/min) and audited; there is no bulk plaintext export by design